All Categories
Featured
Table of Contents
By keeping an eye on cloud resources and their associated expenses, business can make informed decisions that line up with their monetary and strategic goals. In essence, cloud possession management isn't just a side componentit's a foundation of digital improvement techniques. It ensures that businesses can scale effectively, control expenses, and maintain the agility required to adjust to ever-changing market needs.
Improving Cloud Asset Metrics and GovernanceHandling cloud possessions is important for organizations due to: Preventing over-provisioning and eliminating unused cloud resources. Ensuring governance and adherence to industry guidelines. Enhancing workflows and automating resource allowance. Gaining insights into cloud use and preventing shadow IT. Bridging the gap in between on-premises identity systems and cloud-native identity and gain access to management (IAM) services can significantly boost both security and user experience.
By leveraging these combination choices, services can allow single sign-on (SSO) for cloud-hosted workloads. This improves authentication, letting users access resources with their familiar qualifications while keeping central identity management. The secret is to set up IAM controls so that functions and approvals mirror only what each user needsadhering closely to the concept of least opportunity.
To protect sensitive information in the cloud, organizations ought to implement robust encryption both in transit and at rest. Think about these proven approaches: Usage industry-standard procedures such as TLS (Transport Layer Security) to secure information as it moves in between devices and cloud services. Secure data at rest using algorithms like AES-256, making sure files remain secured even if storage resources are jeopardized.
Why Cloud Management Remains Crucial for 2026 ROI
By using these techniques, companies can considerably reinforce their data security posture in any cloud environment. To bolster cloud border security beyond standard procedures, companies can utilize an array of specialized tools.
These tools provide deep package evaluation, evaluate network traffic for indications of harmful activity, and can automatically respond to obstruct or alert on risks as they occur. For even greater visibility, think about options that use real-time traffic analysis and habits tracking. This proactive method assists find anomalies and prospective breaches early, reinforcing your protective perimeter.
A crucial piece in the cloud security puzzle is the shared duty design. This structure plainly delineates where the cloud service provider's security duties end and where yours beginthough the limits shift depending upon your chosen cloud service design: Infrastructure as a Service (IaaS), Platform as a Service (PaaS), or Software Application as a Service (SaaS).
Key Strategies for Better IT Resource Optimization
Nevertheless, you, the client, are accountable for securing whatever you build atop that facilities. This covers from installing OS spots and handling network security controls to configuring firewall programs and protecting your virtual makers with malware protection.: With PaaS, the company extends their protective reach to consist of the platform itselfthink managed running systems and middleware.
You'll require to enforce strong access controls, safe delicate details, and monitor your hosted applications.: SaaS environments offload the bulk of security management to the provider. They're entrusted with safeguarding the application stack, underlying operating systems, and network settings. Your main focus shifts to protecting user gain access to, handling use policies, and safeguarding your company's information within the application.
Take advantage of both built-in and third-party security tools to fortify the locations under your control. Keep gain access to policies, keeping track of practices, and data protection protocols up to date, no matter your cloud usage model. Cloud security isn't one-size-fits-all, however with a clear grasp of your role in this collaboration, you set the phase for a safer, more resistant environment in the cloud.
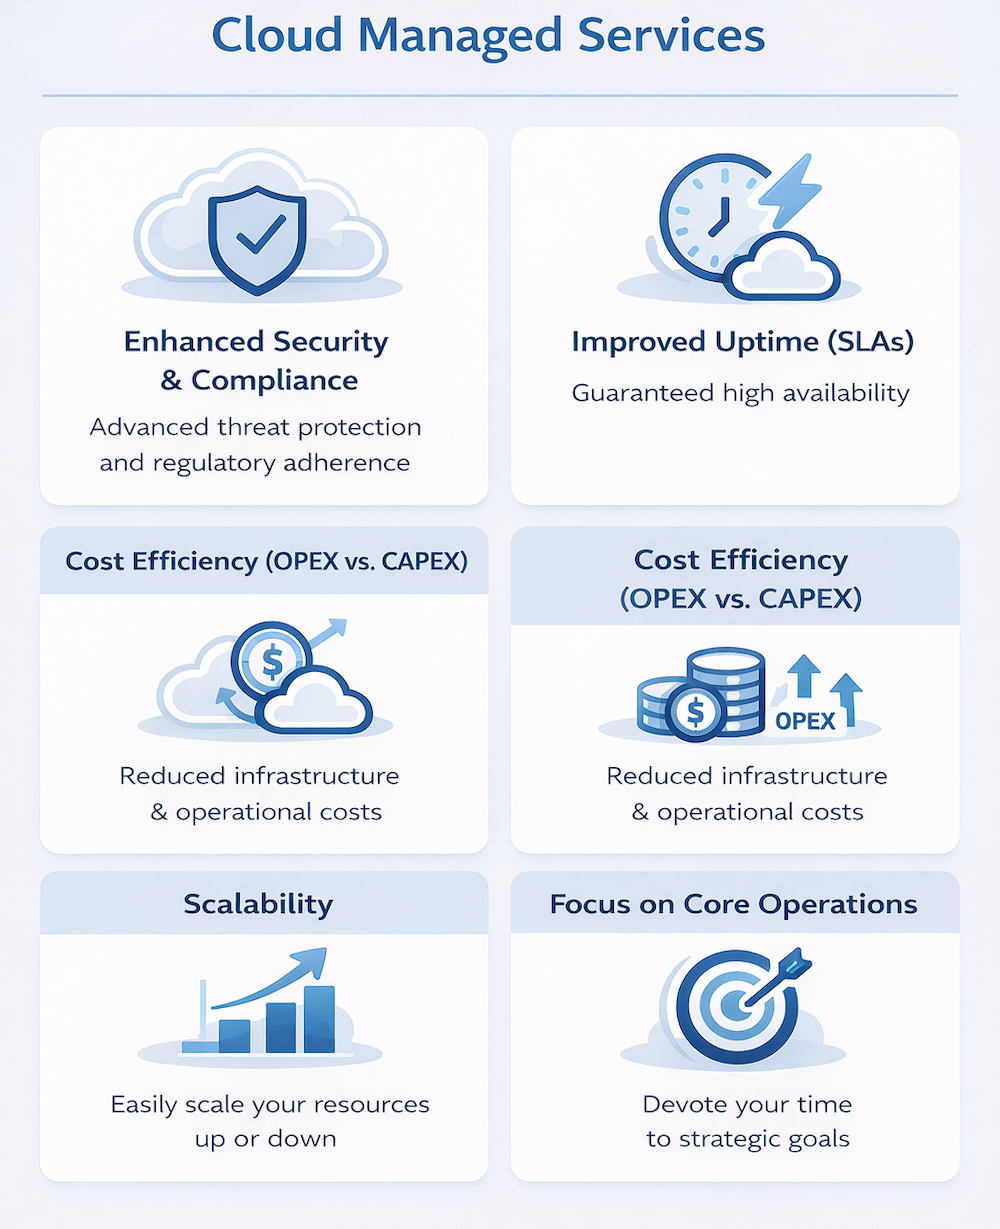
Rather of juggling a patchwork of disparate toolseach with its own control panel and discovering curvesecurity groups acquire one thorough view into endpoints, workloads, identities, and information security. This debt consolidation reduces complexity, making it simpler to track prospective hazards as they unfold, without the requirement to hop in between various user interfaces to get the complete photo.
How to Refine IT Spending for 2026 Budgets
By managing protections, monitoring, and policy release from a main console, teams are empowered to execute consistent security measures throughout accounts, regions, and projects in one go. This method lessens the overhead of handling several licenses, reduces administrative burden, and ensures policies are implemented evenly. Eventually, combining security controls boosts presence, efficiency, and agilitycore active ingredients for equaling developing cloud needs.
Streamlining Resource Allocation Across Enterprise InfrastructuresInstead of leaving teams to rush in the middle of mayhem, these strategies use a clear strategy ought to an event take place. With predefined duties and structured workflows, everyone understands their rolethink of it as designating seats on a lifeboat before the storm hits. Having this structure in place yields numerous crucial advantages: Immediate and collaborated action helps include threats before they mushroom.

Latest Posts
Is Your 2026 IT Budget Optimized?
Aligning Cloud Governance With Strategic Efficiency
Comparing Modern Vs. Traditional Cloud Asset Governance